This comparison is usually framed as which exam is easier. That is the wrong axis, and 2026 made it more wrong: CC and Security+ moved further apart this year, not closer. CC got a new outline on 1 September 2026 with a dedicated governance domain and explicit cloud, zero trust and AI content, and it stopped being free on 20 May 2026. Security+ is unchanged and heading for retirement on 11 June 2027.
Both sets of figures below come from the vendors’ own pages, and we say plainly where a vendor publishes nothing. CC verified 18 September 2026, Security+ verified 12 September 2026.
Side by side, on published facts only
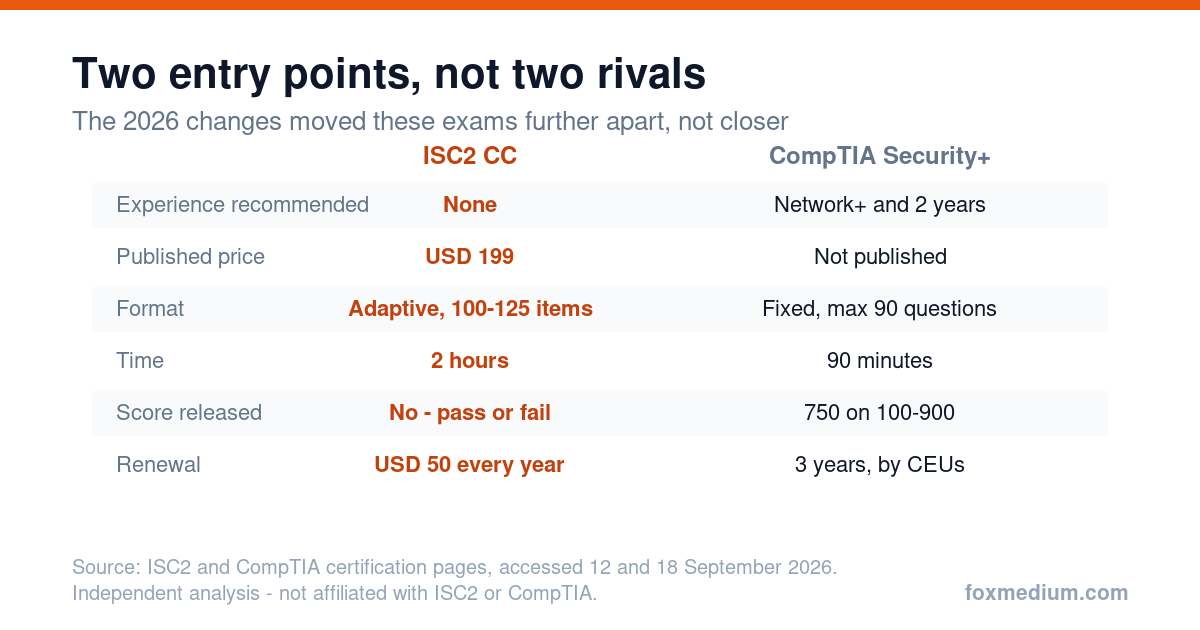
| Experience recommended | CC: none · Security+: Network+ and two years in a security or systems administrator role |
| Published price | CC: USD 199 · Security+: not published on CompTIA’s certification page |
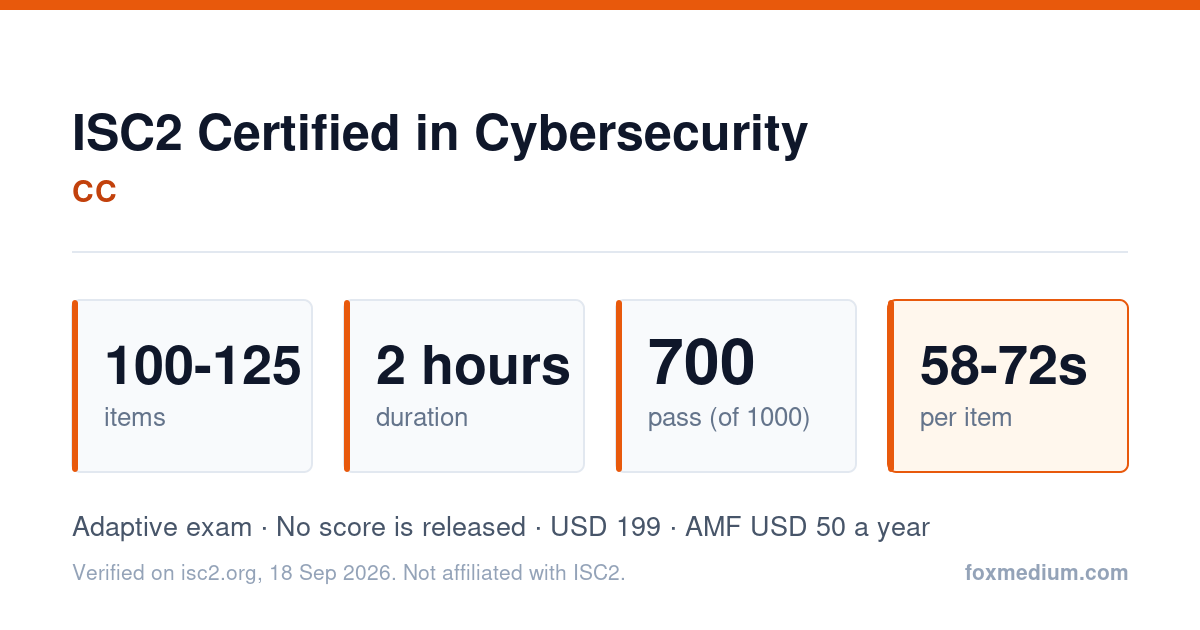
| Format | CC: adaptive, 100–125 items · Security+: fixed form, maximum 90 questions |
| Time | CC: 2 hours · Security+: 90 minutes |
| Per-question budget | CC: 57.6–72 seconds · Security+: 60 seconds at the maximum count |
| Score released | CC: no — pass or fail only · Security+: 750 on a 100–900 scale |
| Renewal | CC: USD 50 every year · Security+: three years, by continuing education |
| Retirement | CC: none published · Security+: English 11 June 2027 |
The choice is about where you are standing
CC exists because ISC2 wanted a route in for people arriving without IT experience, and it is built that way: no experience requirement, no prerequisite, a two-hour adaptive exam. Security+ assumes you have already done the work — CompTIA recommends Network+ and two years in a security or systems administrator role, and the questions are written for someone who has configured things and watched them break.
So the honest question is not which is better. It is which describes you today. Taking Security+ without the background is a harder exam than its reputation suggests; taking CC when you already have three years in IT is paying an annual fee for a credential that sits below where you already are.
Can you settle a CC question in under a minute?
Timed practice against the two-hour limit, with a written explanation for every answer — so the questions you get wrong are the ones you learn from.
- Full-length timed tests that hold you to the real two-hour limit
- An explanation for every answer, right and wrong
- Original questions written from ISC2’s published outline — never real exam content
On Udemy · lifetime access · 30-day refund policy applies
Straight answer before you click: our CC question bank was written against the previous exam outline and is being rebuilt for the domains that took effect on 1 September 2026. Until that is done it is useful for the fundamentals that did not change — and it does not yet cover the new governance, cloud and threat-intelligence material. We would rather tell you that here than have you find out afterwards.
Comparing entry points? CompTIA Security+ practice tests. Heading for cloud instead? AWS Solutions Architect Associate practice tests.
Two differences that are easy to underestimate
You get a score from one and not the other. Security+ reports 750 on a 100–900 scale. CC reports nothing at all — ISC2 provides no scores, only a pass or fail, with proficiency levels by domain if you fail. If you find feedback motivating, that is a real difference in the experience.
The renewal shapes differ. CC costs USD 50 every single year, starting immediately. Security+ runs three years and is renewed by continuing education, with no annual invoice. Over six years, the CC fee is a recurring line item; the Security+ obligation is a periodic effort.
Take CC first if…
- You are coming from outside IT and need a credible, accredited starting point with no gatekeeping on experience.
- You want the current curriculum. CC’s outline was rewritten three weeks ago and now covers cloud, zero trust, threat intelligence and AI explicitly.
- You want a published price you can budget against before committing.
Take Security+ first if…
- You already have IT experience around the level CompTIA describes.
- The roles you are applying for name it. It remains the more commonly specified of the two in job descriptions.
- You prefer a fixed-form exam with a reported score and a three-year cycle rather than an annual fee.
Where practice questions fit
Practice questions are a diagnostic, not a syllabus. Their job is to find the domain you are weak in and to train you to commit to an answer quickly, which matters more on an adaptive exam than on a fixed one. Used that way — timed, reviewed, and written from the published outline — they are the most efficient preparation available in the last few weeks.
One caution that matters more than it appears to. Sites offering “real exam questions”, brain dumps or leaked CC content are selling you a violation of the ISC2 Examination Agreement and Non-Disclosure Agreement, and ISC2 states it may revoke certifications and ban you from earning future ones. They are also stale by construction: the outline changed on 1 September 2026, so anything harvested before then describes an exam that no longer exists.
Practise under the clock, not just the syllabus.
The short answer
If you are starting from zero, start with CC. If you have been doing IT work for a couple of years, go straight to Security+ and skip the annual fee. Full published parameters for each: our ISC2 CC exam guide and our CompTIA Security+ (SY0-701) exam guide.
Frequently asked questions
Should I take ISC2 CC or CompTIA Security+ first?
CC if you are starting from outside IT and want a recognised entry point with no experience requirement. Security+ if you already have IT experience and are targeting roles that name it, since it is written for someone with around two years of experience.
Which is cheaper, CC or Security+?
CC publishes its price: USD 199, plus a USD 50 annual maintenance fee. CompTIA does not publish the Security+ voucher price on its certification page, so a like-for-like comparison is not possible from vendor sources.
Is CC easier than Security+?
They are aimed at different starting points rather than sitting on a single difficulty scale. CC requires no experience; Security+ recommends Network+ and two years in a security or systems administrator role.
Do they cover the same material?
Less than they used to. Since 1 September 2026 CC has a dedicated Security Governance domain and explicit cloud, zero trust and AI content. Security+ remains broad across operations, threats, architecture and program management.
Can I do both?
Yes, and people often do, though the renewal obligations differ: CC is a USD 50 fee every year, while Security+ runs three years on continuing education.
Sources. All exam parameters above come from ISC2’s own CC certification page and exam outline (effective 1 September 2026), its article on the updated exam, its exam policy pages and its Annual Maintenance Fee page, accessed 18 September 2026, together with its 22 April 2026 press release on the conclusion of the One Million Certified in Cybersecurity programme. Exam parameters change; if you spot a discrepancy, check ISC2’s page and tell us so we can correct it.
Disclosure and disclaimer. FoxMedium publishes independent study material. Our practice tests are not official ISC2 content and are not endorsed by, affiliated with, or representative of ISC2 or the official certification examination. All questions are original and written from publicly published exam outlines. We do not host or distribute real exam content. Links to our courses earn us revenue if you enrol. ISC2, CC, Certified in Cybersecurity, CISSP and all related trademarks belong to their respective owners.